Summary
Chainloop Evidence Store can be configured to generate signing certs by using EJBCA as the certificate authority, when signing in “key-less” mode: EJBCA is a popular open source PKI, check it out at https://www.ejbca.org/.Prerequisites:
If your organization doesn’t have it already, you can follow these tutorials for a basic setup of EJBCA PKI solution. Requirements:- EJBCA is deployed following the Quick Start Guide - Start EJBCA Container with Client Certificate Authenticated Access
- EJBCA is configured for issuing signing certificates. Check the certificate request and installation steps at Sign Container Images with Cosign and SignServer
- EJBCA Certificate Management APIs are enabled.
Configure Chainloop to use EJBCA as CA
Checkejbca_cA section in Chainloop configuration options. In particular, set these values in your config.yaml (these values are also mapped to the chart values.yaml file):
Signing Chainloop attestations with EJBCA issued certificates
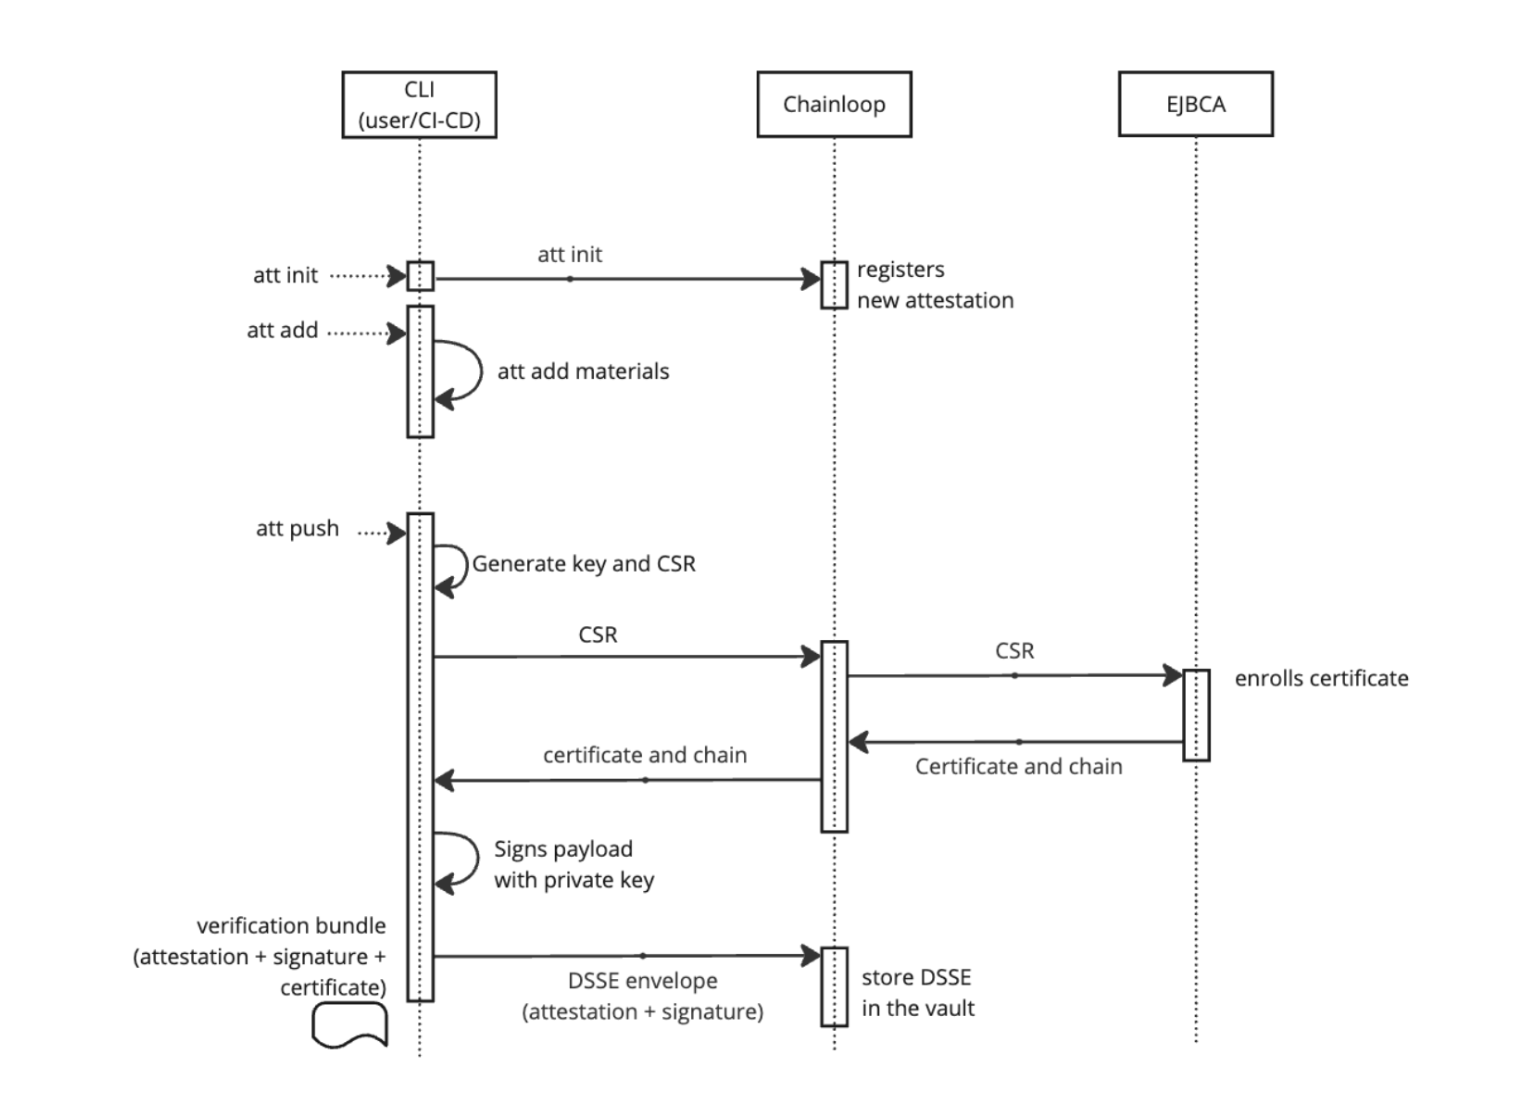
Using the following command (note that nokey is provided), the following sequence of events will happen:
- Chainloop CLI creates a certificate request, and sends it to Chainloop
- Chainloop forwards the request to EJBCA’s
v1/certificate/pkcs10enrollAPI, which generates a new short-lived certificate for signing - Chainloop CLI signs the In-toto payload, and sends the statement to Chainloop for storage.